
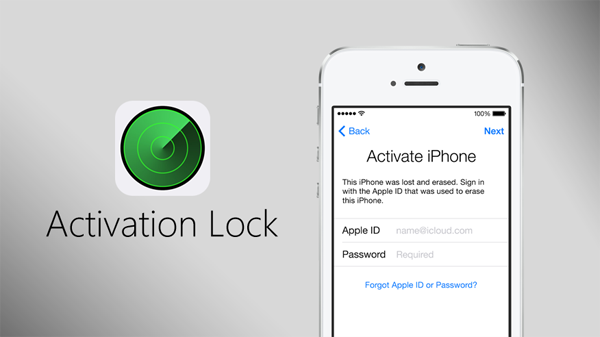
Researchers have discovered how to bypass the security lock in iOSThey stated this in their reports published this week. According to the reports, they have successfully bypassed the activation lock Applu on iPad and iPhone. This step will make the device completely insecure. First reports of potential vulnerability iOS The devices appeared in early November, when one of the security experts tried to bypass the activation lock on an iPad purchased on the eBay auction server.
Researchers have managed to bypass the activation lock on the iPad. In early November, security expert Hemanth Joseph warned about the vulnerability of some iOS device – he tried to bypass the activation lock on an iPad he bought on eBay. Joseph discovered a method to break the security software by entering an extremely long string of characters into the iPad’s Wi-Fi settings. Activation lock was designed and implemented with iOS 7 and was intended to prevent thieves and other unauthorized users from accessing stolen or lost iOS device. It is automatically activated by turning on the "Find My" feature. iPhone". Once the feature is activated, any user who would like to try to access the device must turn off the "Find My" feature. iPhone" , erase the device or deactivate it, they must enter the correct access details. ProThe deactivation process is associated with performing a checkApple ID and passwords on servers Applu, which requires an internet connection. And it was at this point that Joseph discovered a loophole.
You might be interested in

When the locked device is turned on, iOS prompts the user to connect to the nearest Wi-Fi network. Joseph was able to exploit the Activation Lock bug by selecting the “Other Network” option and entering a long string of characters in the “Name,” “Username,” and “Password” fields. These fields have no character limit.
The subsequent freezing is completely nestAlthough it was designed to bypass Activation Lock, Joseph was able to hack the security app by simply closing and opening the Smart Cover on his iPad, gaining access to the home screen. This security flaw was supposed to be fixed with the release of iOS 10.1.1, SecurityWeek reported that researchers at Vulnerability Labs were able to gain access to the device by using screen rotation and Night Shift mode. You can see the details of the entire operation in the following video.
Whether also about this error Apple knows, it is not yet known, as well as whether this security gap will be filled in iOS 10.2.
Source: Appleinsider.com






O2 was blocked again imessage with new phones. My wife and I have two new sevens and suddenly imessage are waiting for activation. It is evidently a widespread problem again, but I understand that for the article it nestoh...
From my experience it's not just O2 I have T-Mobile and iMessage They are doing exactly the same thing to me, I tried contacting support, I was in iStyle and nothing helped.
I have exactly the same problem. I haven't found a solution yet. Yesterday, everything stopped working for me. iMessage tied to a number. I have tried the instructions found on various discussion forums, but so far without any results.