
Security experts reported that a key component of the company's location services Apple contains a "really serious vulnerability" that allows, among other things, the tracking of troop movements. The flaw could also allow potential attackers to discover the location of anyone using a mobile Wi-Fi router, such as in RVs and travel routers that are sometimes used by business travelers.
You might be interested in
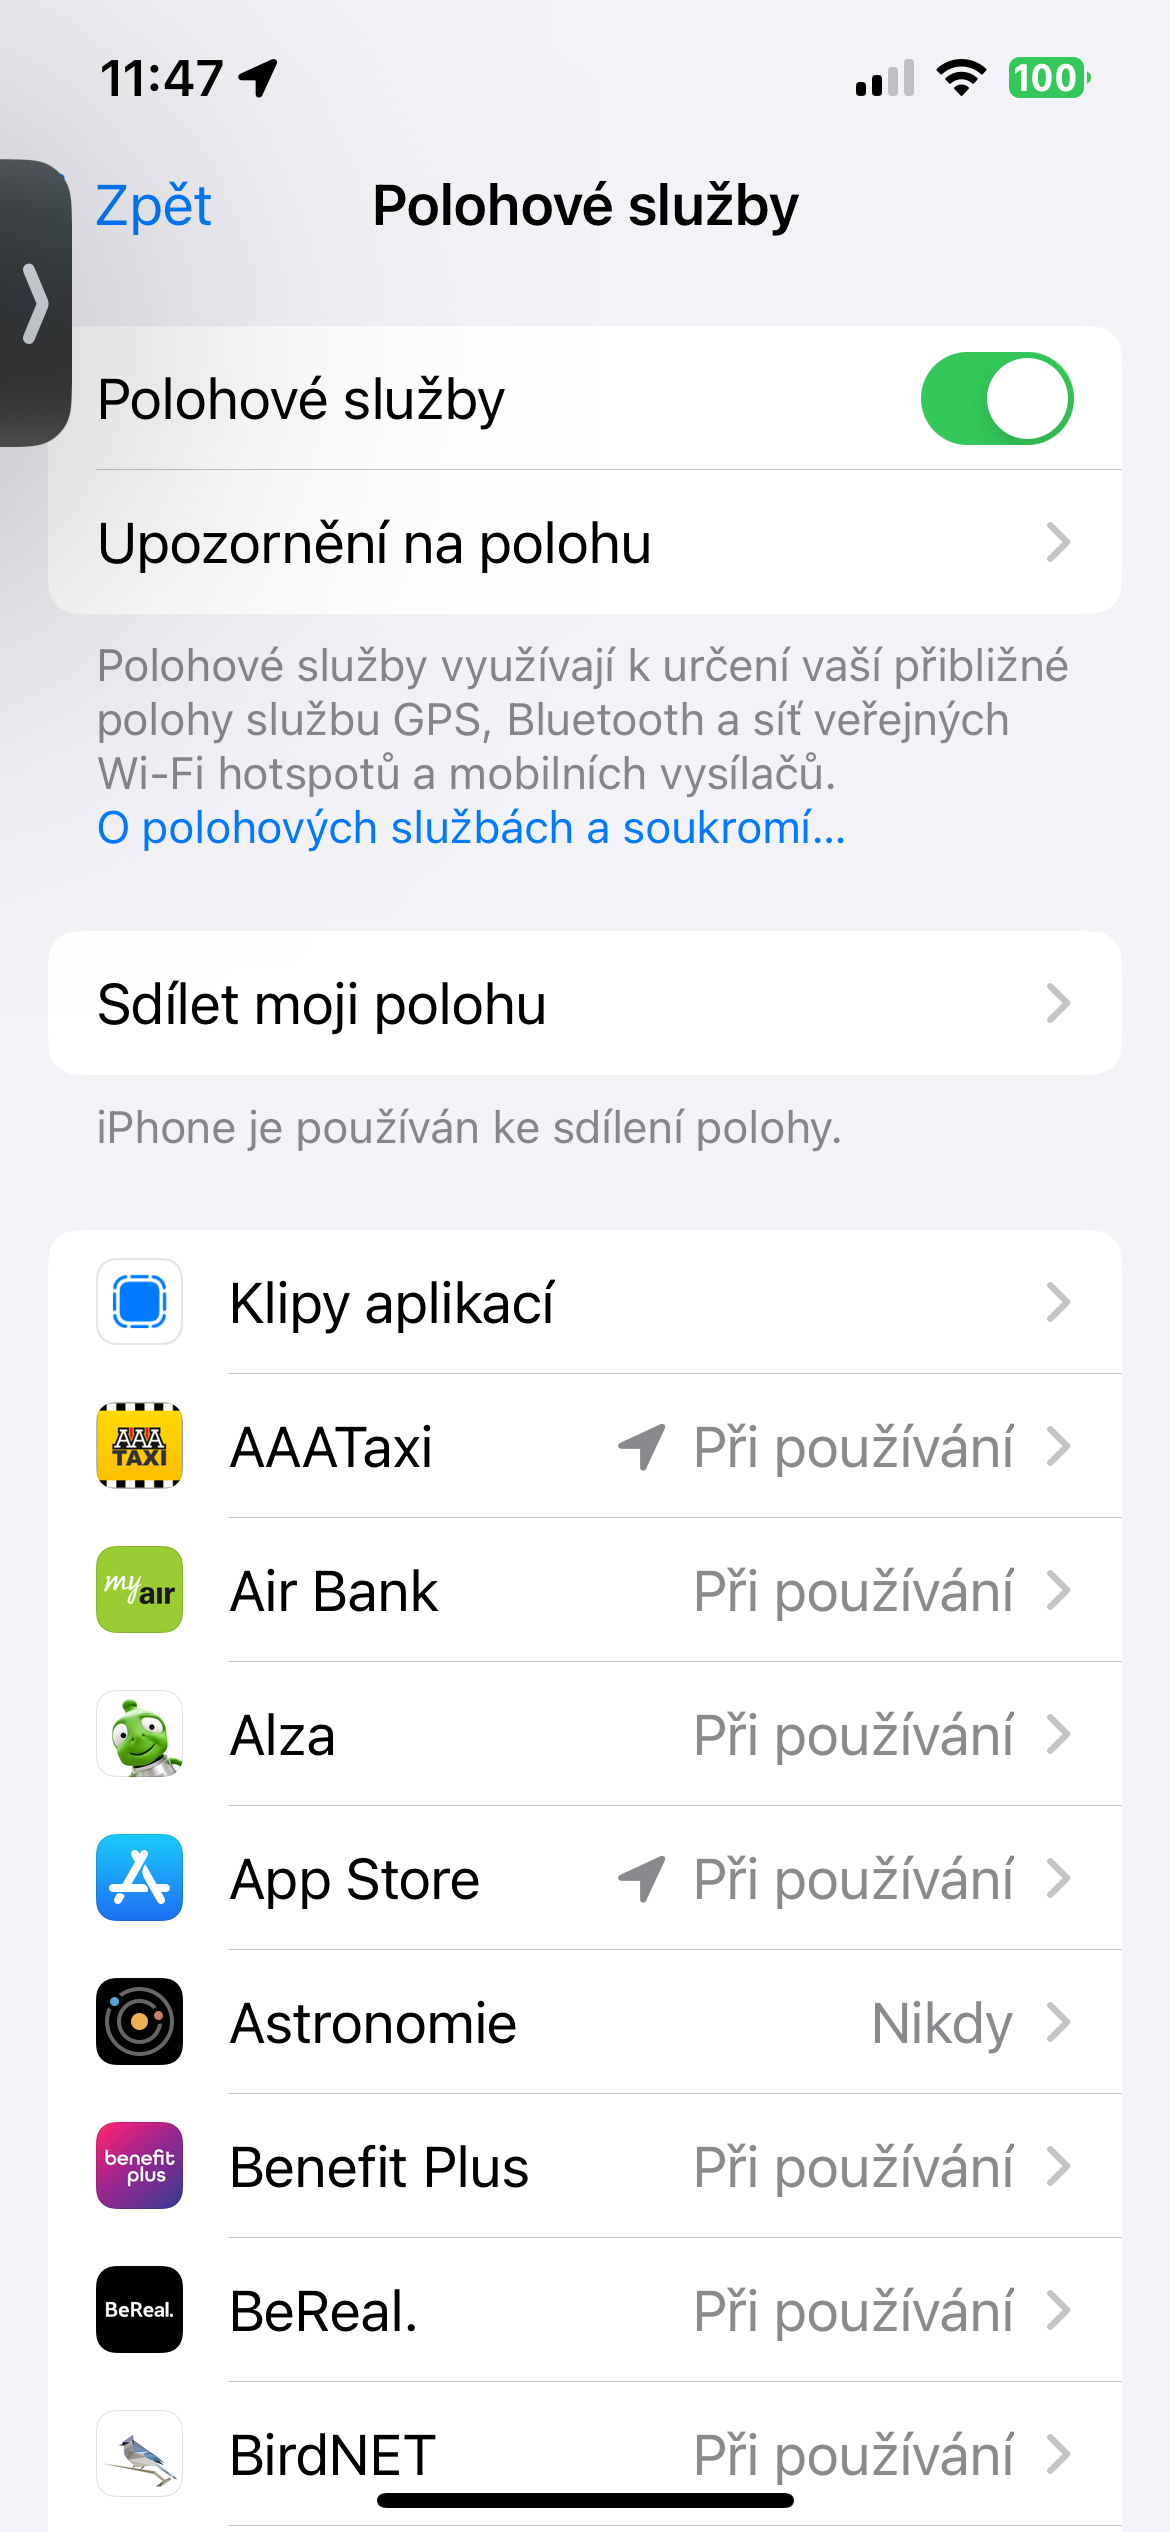
How do location services work on Apple devices? The primary technology is GPS, but it is not the only option. For example, in urban areas, tall buildings can make it difficult to receive very weak signals from GPS satellites, so Wi-Fi-based positioning systems (WPS) are another key method used by mobile devices.
WPS uses a global database of nearly 500 million Wi-Fi routers. What's important: it's not just public routers that can actually be accessed, but all BSSIDs that WPS systems can see. This includes, for example, your home Wi-Fi router. The devices don't get any access to your router, but they can detect it and find out its exact location based on the database. In the same way, they maintain their own WPS databases as well Apple, so Google. The method they use is basically the same - they record the BSSIDs in the area, measure the strength of each signal, and then compare that data to the WPS database to determine where the mobile device is located.
In the way the device Apple and Google perform this task, however, there is one major difference - and that is where the privacy issue arises.
Vulnerability in location services from Applu
Google devices use WPS as follows: an Android phone records the BSSIDs it can see and their signal strengths and sends this data to a Google server. The server uses the WPS database to calculate the phone's location and sends it to the phone.
However, security experts from the University of Maryland found that the device Apple they use a different approach. The company's WPS service Apple also accepts a list of nearby BSSIDs, but instead of calculating a device's location based on a set of observed access points and their received signal strengths and then reporting that result to the user, the company's API Apple returns the geographic locations of other BSSIDs that are near the requested one. It then uses approximately eight of these BSSIDs to determine the user's location based on known landmarks.
Essentially, Google's WPS system calculates the user's location and communicates it to the device. Google's WPS service Apple it provides its devices with enough data about the location of known access points in the area that the devices can make this estimate on their own.
On-device processing is one of the company's business drivers Apple and seems to be safer - but this is where the problem arises.
The aforementioned University of Maryland experts theorized that they could take advantage of the breadth of the company's API Apple to map the movement of individual devices to and from virtually any defined area in the world. The pair of UMD experts said they spent a month early in their research constantly polling the API, asking it for the location of more than a billion randomly generated BSSIDs.
Gallery



They found that although only about three million of these randomly generated BSSIDs were known to the company's Wi-Fi geolocation Apple, Apple also returned an additional 488 million BSSID locations already stored in its WPS from other searches. As a result, they basically managed to get hold of the WPS database.
When viewing the positions returned by WPS to the company Apple between November 2022 and November 2023, the aforementioned researchers found that they had a near-global overview of the locations of more than two billion Wi-Fi access points.
By focusing on other smaller areas indexed by the company's location API, experts said Apple they could track how Wi-Fi access points moved over time. ProCould this be a big problem? University experts said that geofencing active conflict zones in Ukraine allowed them to determine the location and movement of Starlink devices used by both Ukrainian and Russian forces.
The risk was greatest with Starlink mobile hotspots, and the company is now addressing this by randomizing the BSSIDs used.
If you want to prevent that Apple even Google added your router to their databases, you can add nomap to your SSID. For example, if your wifi SSID is currently John Appleseed Home, you can change it to John Appleseed Home_nomap – this will give the company Apple even Google will tell you that your router is out of bounds and they will not collect your BSSID.
You might be interested in
Company Apple said it would take steps to limit the number of queries that could be made on its database to mitigate the risk.
Vulnerability in Apple Location Services is a serious issue that could be misused to track the movements of individuals and groups. Apple is taking steps to correct the problem, but users should also consider taking steps to protect their privacy, such as adding nomap to their SSID.







Apple so he's been stepping into it lately. But this will probably be a long-term problem and it was discovered recently. I wonder that Apple updates various security bugs and skips this one entirely. He doesn't know about it or he knows very well. Security probably won't be their strong point lately or has it never been? Hard to say
Don't worry, we'll have super AI generated emoji, add some LGBT+++++++++++ wallpapers and no one will even sigh at all the mistakes and snooping anymore - we're saved.
And everyone will be happy